Cybersecurity built for organizations that take trust seriously

Arann Tech helps regulated organizations in Canada and the US build defensible security programs, satisfy auditors and clients, and adopt AI responsibly. Senior expertise, plain-English advice, no enterprise overhead.

CISSP-Led Practice
Healthcare & Financial Specialization
100% Vendor-Independent
Security and compliance shouldn't be a guessing game.

For growing healthcare providers, financial firms and professional services businesses, a failed vendor audit or a single breach can stall deals, trigger regulators and disrupt operations.

You probably don't need a large outsourced SOC and thousands of noisy alerts. You need a dedicated team of senior advisors who build your policies, keep your risk register current, hold your vendors to account and explain it all to your board in plain language.

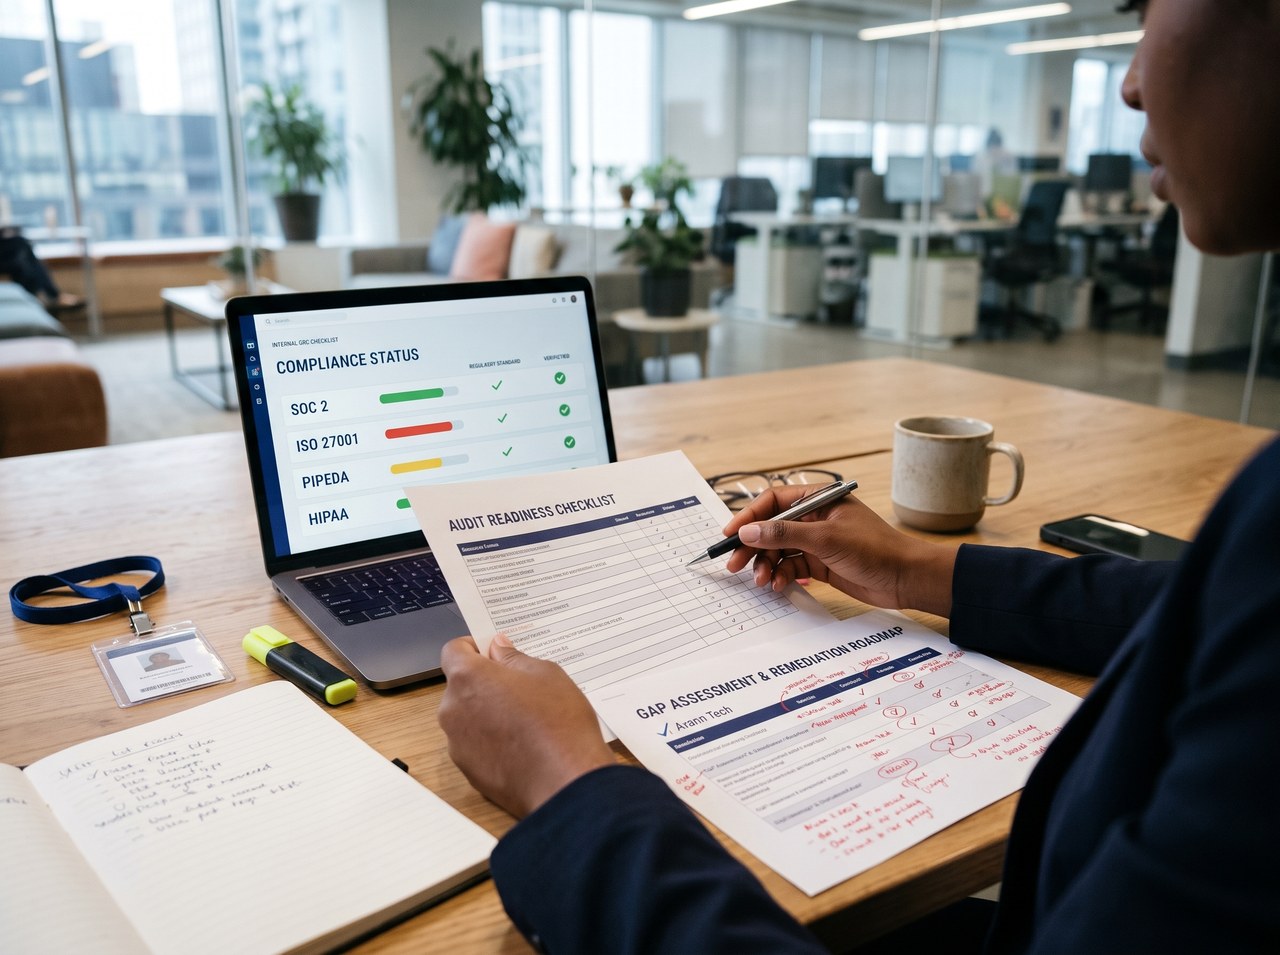
Audit readiness without last-minute scrambling
Defensible policies that reflect real-world operations
Vendor scrutiny before third parties jeopardize your data
Security and Compliance Risk Assessment & Audit Preparation

Vendor-Neutral, Defensible Security

Arann Tech is a vendor-neutral advisory firm. We don't resell software or sell on fear. We design and maintain security programs aligned with ISO 27001 and NIST CSF so you can demonstrate control to auditors, clients and regulators.

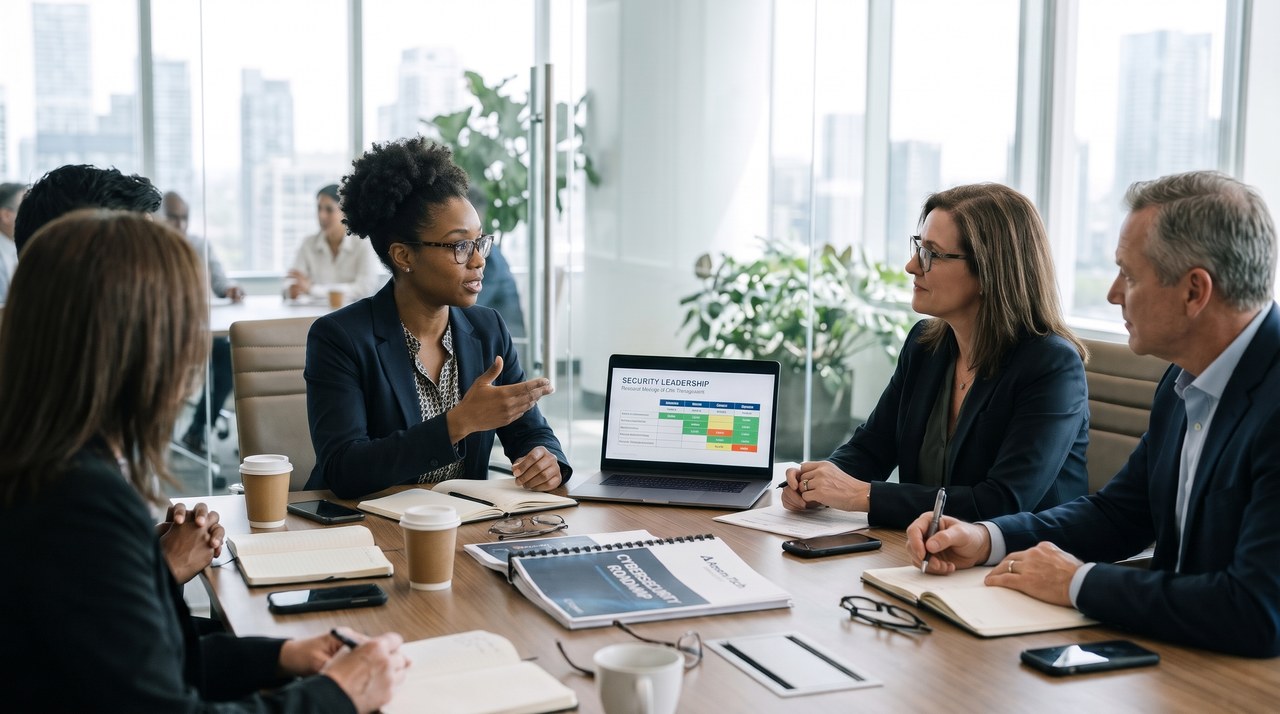
Security Leadership & GRC
Practice 01

Security Leadership & GRC

Ongoing executive-level security leadership, policies, and a living risk register. Readiness for PIPEDA, HIPAA, SOC 2 and ISO 27001.

  • Executive advisory retainers
  • PIPEDA, HIPAA & SOC 2 roadmaps
  • Living enterprise risk registers
Risk & Threat Modeling
Practice 02

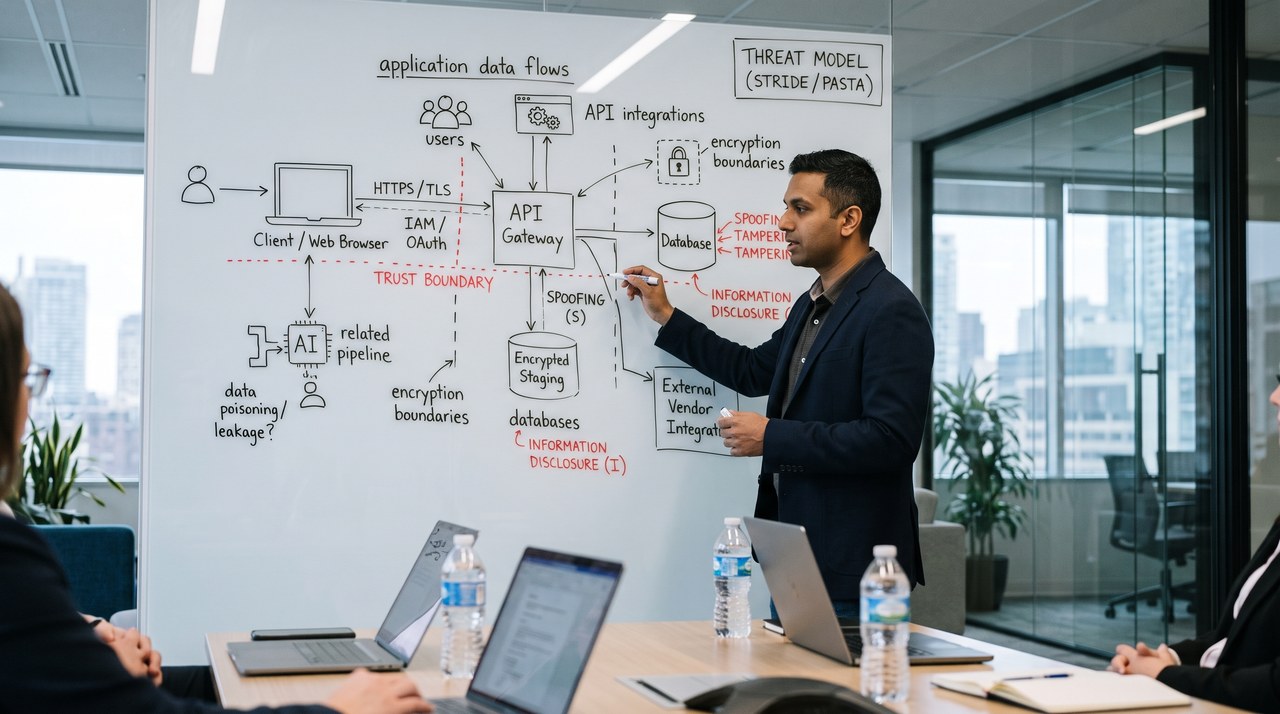
Risk & Threat Modeling

Structured reviews of how your applications and infrastructure are designed, using STRIDE and PASTA, with prioritized remediation plans your engineers can act on.

  • Architecture security reviews
  • STRIDE & PASTA assessments
  • Engineer-ready remediation steps
Third-Party Risk Management
Practice 03

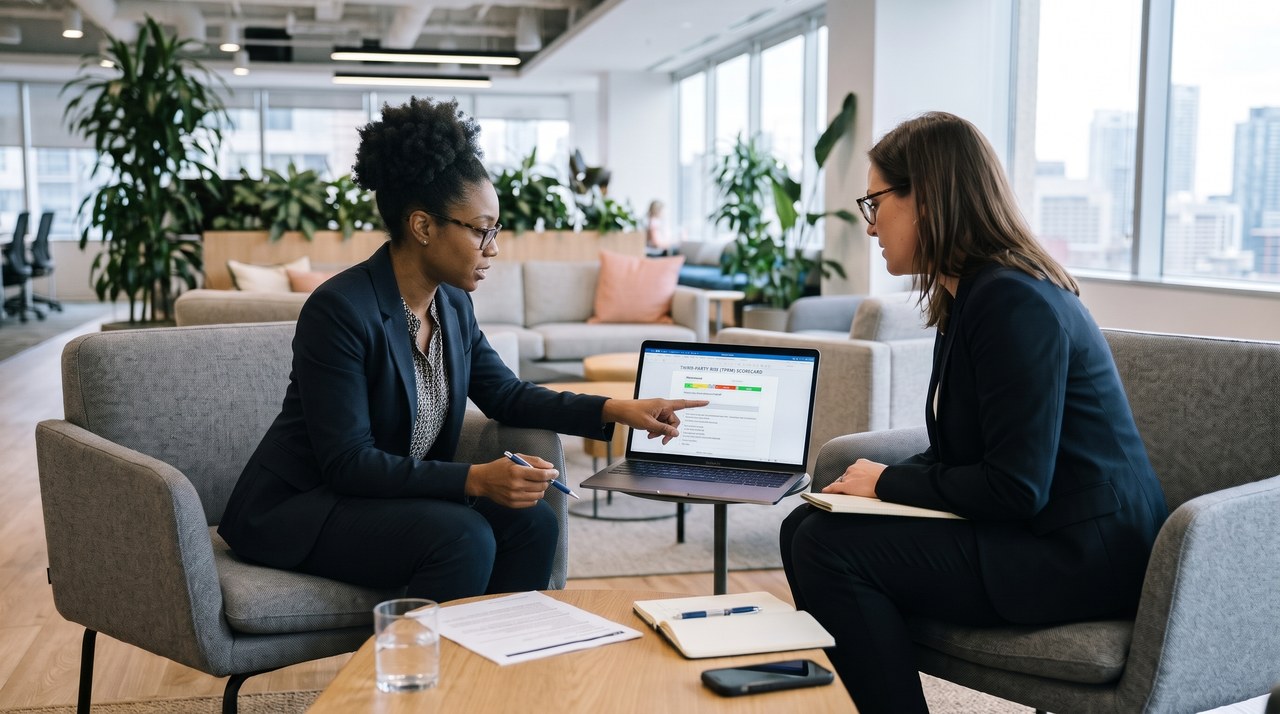
Third-Party Risk (TPRM)

Vendor due diligence, from SOC 2 report analysis to security questionnaires, so you know what you're accepting before you sign.

  • Vendor SOC 2 & ISO report reviews
  • Security questionnaire vetting
  • Pre-contract risk negotiation support
AI Governance & Security
Practice 04

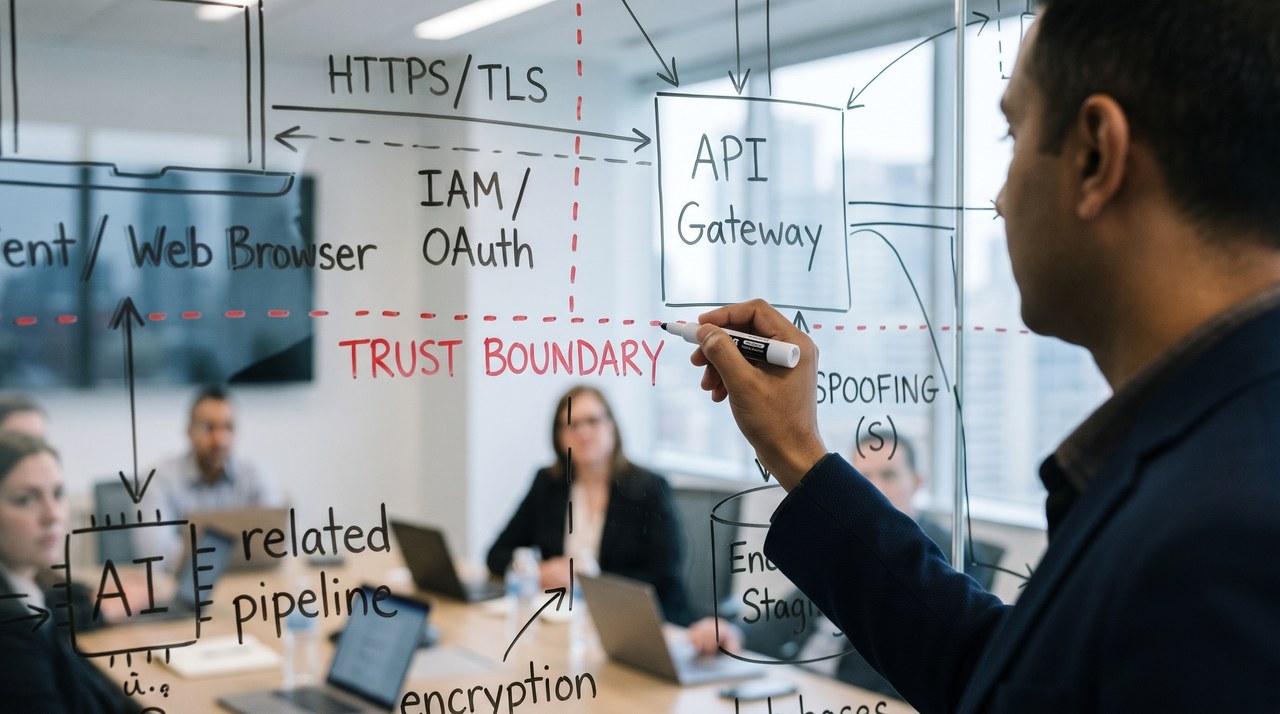
AI Governance & Security

Policies, risk assessments and guardrails for generative AI, aligned with ISO 42001 and the NIST AI RMF.

  • GenAI Acceptable Use policies
  • ISO 42001 & NIST AI alignment
  • Data leakage defense & guardrails

Built for Regulated & Client-Scrutinized Organizations

Calibrated to the specific compliance requirements and audit pressures of mid-market organizations.

Healthcare Providers

Clinics, specialized medical practices, and healthcare technology providers managing sensitive patient health information while staying compliant with PHIPA, PIPEDA, and HIPAA.

Financial Services

Lenders, wealth advisory practices, specialized insurers, and fintech innovators who must demonstrate operational resilience and rigorous third-party risk management under OSFI guidelines.

Explore All Regulated Sectors →

A Boutique Advisory Model Built for Direct Access & Independence

Traditional cybersecurity firms pitch with senior partners and deliver with junior analysts. We deliver senior CISSP-level leadership, plain-English guidance, and true independence from vendor software commissions.

01

Senior-led teams

Every engagement is led by an experienced, certified practitioner, not handed to a junior pool.

04

Independent

We have no products to push and no referral fees. Our recommendations are 100% objective and client-first.

02

Plain English

Findings written for boards and executives as well as engineers, translating complex risk into clear action.

03

Right-sized

Programs built for your size, budget and regulatory reality—never bloated enterprise overhead.

05

Continuity

A team behind your account, so your security program doesn't depend on one person's calendar.

CISSP-Led Practice
CompTIA Security+ Certified
ISO 27001 & NIST CSF Aligned
Serving Canada & the US
Next Steps

Not sure where to start?

Book a free 30-minute call. We'll review your obligations and top risks and tell you plainly what you need and what you don't.